

Port Forwarding and Triggering
Configure port forwarding and port triggering for proxy and modem access.
Learn how to configure port forwarding on your router so external devices can access your Proxidize server, local dashboard, and generated proxies.
What Is Port Forwarding?
Port forwarding is a router setting that allows traffic from the internet to reach a specific device inside your local network.
Most routers block incoming internet traffic by default. This protects your local devices, but it also means external users cannot reach services running on your Proxidize server unless the correct ports are forwarded.
For Proxidize, port forwarding may be needed when:
You want to access the local Proxidize dashboard from outside the network.
You want to use generated proxies from outside the local network.
You want SSH access to the Proxidize server from outside the local network.
Your Proxy Builder setup is configured to run locally instead of through the Cloud Dashboard.
Port Forwarding vs Port Triggering
Port forwarding
Permanently forwards a public port to a specific local device and port.
Yes
Port triggering
Temporarily opens a port after outbound traffic triggers it.
No
For Proxidize, use port forwarding because the router must consistently send traffic to the Proxidize server.
Before You Start
Before creating port forwarding rules, make sure you have:
Access to the router settings page.
The Proxidize server's reserved local IP address.
The public IP address or DDNS hostname users will connect to.
The dashboard, SSH, or proxy ports you want to expose.
Confirmation that your ISP allows inbound traffic on those ports.
We strongly recommend reserving the Proxidize server's local IP before setting up port forwarding. See Local IP Reservation (DHCP).
Understand the Connection Path
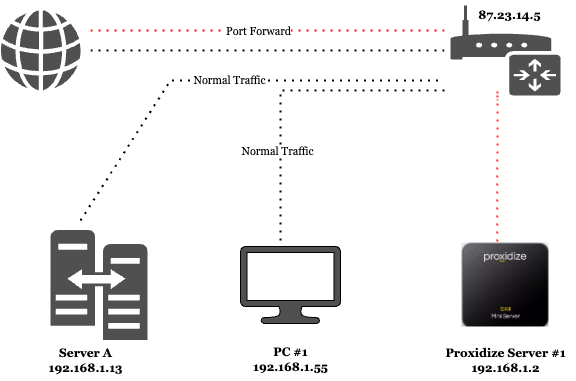
Without port forwarding, external traffic reaches your router and stops there.
With port forwarding, the router sends traffic from a public port to the Proxidize server's private IP and internal port.
Example:
Public IP / host
87.73.14.5
Public proxy port
2001
Proxidize server local IP
192.168.1.25
Internal proxy port
2001
In this example, a remote proxy user connects to:
87.73.14.5:2001
The router forwards that traffic to:
192.168.1.25:2001
Common Proxidize Ports
Local Proxidize dashboard / web interface
80
Forward if you need dashboard access from outside the local network.
SSH / terminal access
22
Forward only if you need remote terminal access.
HTTP Proxies
2001 to 200x
Forward if locally generated proxies must be usable from outside the local network.
SOCKS5 Proxies
3001 to 300x
The generated proxy port range depends on the number of proxies.
For example:
If you have 1 generated proxy, you may need port
2001for HTTP Proxy and port3001for SOCKS5 Proxy.If you have 5 generated proxies, you may need ports
2001-2005for HTTP Proxies and3001-3005for SOCKS5 Proxies.If you have 20 generated proxies, you may need ports
2001-2020for HTTP Proxies and3001-3020for SOCKS5 Proxies.
Confirm the actual proxy ports shown in your Proxidize dashboard before creating rules.
Create Port Forwarding Rules
The exact router menu depends on the router model, but the general process is similar.
Enter the rule details.
Service name
A clear name, such as Proxidize Dashboard
External port
The public port users will connect to
Internal IP
The reserved local IP of the Proxidize server
Internal port
The Proxidize service port on the server
Protocol
TCP, or Both if your router requires a combined option
Status
Enabled
💡Note: Some routers allow you to specify a port range to be forwarded. For example, you could forward ports
2001-2005in one rule.
TP-Link Example
On many TP-Link routers, port forwarding is located under:
Advanced > NAT Forwarding > Virtual Servers
From there:
Click Add.
Enter a service name.
Enter the external port.
Enter the Proxidize server's reserved local IP.
Enter the internal port.
Select the protocol.
Enable the rule.
Save the configuration.
Example Rules
Use these examples as a starting point. Replace the internal IP with your Proxidize server's reserved local IP.
Dashboard access
80
192.168.1.25
80
TCP
SSH access
22
192.168.1.25
22
TCP
Proxy 1
2001
192.168.1.25
2001
TCP
Proxy 2
2002
192.168.1.25
2002
TCP
Proxy 3
2003
192.168.1.25
2003
TCP
💡Note: If your router supports port ranges, you may be able to forward the proxy range in one rule.
Example:
Proxy range
2001-2020
192.168.1.25
2001-2020
TCP
Use the Correct Host for Remote Access
After forwarding ports, external users should connect using your public IP address or DDNS hostname.
For dashboard access:
http://87.73.14.5
or:
http://mydomain.ddns.net
For generated proxies:
Host
87.73.14.5 or mydomain.ddns.net
Port
2001
💡Note: Do not use the Proxidize server's private IP, such as
192.168.1.25, when connecting from outside the local network.
Test Port Forwarding
After saving the rules:
Disconnect your test device from the local network, or use a device on a different internet connection.
Test the dashboard, proxy, or SSH connection using the public IP or DDNS hostname.
Confirm the service responds.
⚠️Warning: Testing from inside the same network using the public IP may not always work because some routers do not support NAT loopback.
ISP and Network Limitations
Port forwarding may not work if:
Your ISP blocks inbound traffic on the selected ports.
Your ISP uses CGNAT.
Your router is behind another router.
Your public IP changed and you are connecting to the old address.
The forwarding rule points to the wrong internal IP.
If your router WAN IP does not match your public IP lookup, check for CGNAT or double NAT before troubleshooting the rules further.
For more details, see Dynamic Public/WAN Addresses.
Troubleshooting
Dashboard does not open remotely
Confirm port 80 is forwarded to the Proxidize server's reserved local IP.
Generated proxy does not connect remotely
Confirm the specific proxy port is forwarded to the Proxidize server.
SSH does not connect remotely
Confirm port 22 is forwarded and SSH is installed and enabled on the server.
Forwarding worked before but stopped
Check whether the server local IP or public IP changed.
Router rule looks correct but port is closed
Check for ISP blocking, CGNAT, double NAT, or firewall rules.
Public IP works locally but not externally
Test from a different network and check whether the router supports NAT loopback.
Related Articles
Need Help?
If you have any questions, concerns, or need further clarification, feel free to reach out to us via live chat or email us directly at support@proxidize.com.
Last updated
Was this helpful?